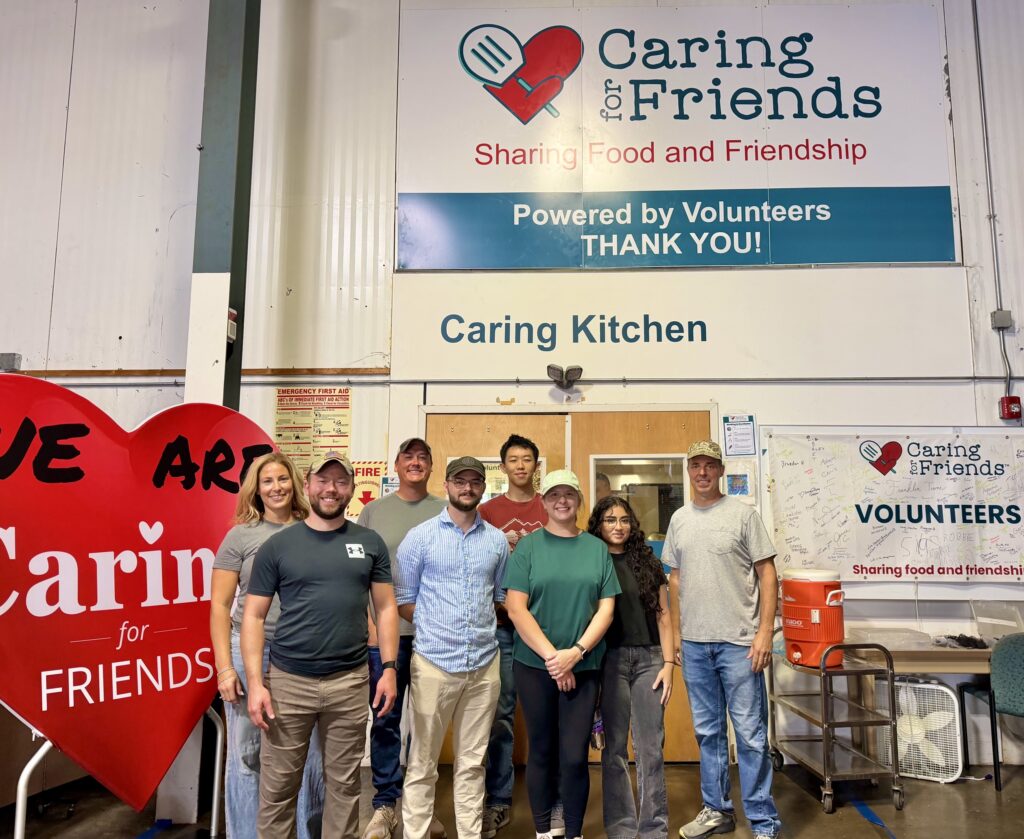
Every year, the Behunin & Associates team takes a day away from the office for our annual service day. This year, eight of us spent it with Caring for Friends, a Philadelphia nonprofit that’s been feeding people and fighting isolation in the area for almost 50 years.
The non-profit organization started in 1974, when founder Rita Ungaro-Schiavone began delivering homecooked meals to homebound neighbors out of her own home. It’s now grown into a network of 10,000 volunteers and 200 food pantries across five counties, running a homebound meals program, homeless outreach, and a food bank.
The Summer Sandwich Program
We helped out with their Summer Sandwich Program, which supports school kids, families, seniors, veterans, and others who need extra help during the summer months, when school meal programs aren’t running. Over the course of the day, our team of eight assembled and packaged 672 sandwiches for distribution across the Philadelphia area.
It’s not complicated work — spreading, stacking, wrapping, boxing — but it adds up fast, and it’s a good reminder of what a small group of people can get done in a few hours when the goal is straightforward.
We’re glad we could contribute to what Caring for Friends does year-round, and we’re already looking forward to next year’s service day.
What Actually Matters in IT Audit: Scope, Controls, Documentation, and the AI Question
A strong IT audit goes beyond compliance and helps organizations focus on what matters most.
Greater value comes from understanding which systems truly belong in scope. It also requires recognizing where control gaps tend to appear and where teams are most likely to struggle.
Documentation is often a bigger challenge than expected and a common source of audit issues.
Emerging technologies like AI are reshaping the control environment and introducing new risks to manage.
An IT audit can easily turn into a checklist exercise, but its real value comes from focusing on what actually matters.
For most organizations, that means understanding which systems belong in scope, addressing the risks that matter most, documenting controls clearly, and thinking ahead about how AI may change the environment.
The teams that get the most from the audit process are usually not the ones doing the most documentation, but those who understand where risk actually sits and where audit scrutiny is most likely to fall.
What systems should be in scope for an IT audit?
One of the most important parts of an IT audit is defining scope correctly. In a financial reporting context, systems are typically in scope if they support transactions or data that flow into the financial statements.
Just as important are the supporting systems around them. A user access management system may be relevant because it governs access to financial systems. A help desk ticketing system could be included in the scope of the audit because it tracks requests, approvals and issues affecting those systems. In an operational audit, the same logic applies: if a system touches the process under review, it may belong in scope.
If scope is too narrow, important risks may be missed. If it is too broad, teams spend time documenting systems that do not materially affect the process. A good scoping process helps organizations stay grounded in what is relevant to the audit.
Where teams usually struggle: Segregation of Duties and compensating controls
Segregation of duties is one of the most common areas of IT audit focus, and one of the hardest for smaller IT teams to implement well.
In larger organizations, responsibilities may be divided among developers, implementers, reviewers, and approvers. Smaller teams often do not have that luxury. If there are only a few people in the IT department, those same individuals may need to handle multiple responsibilities.
When strict segregation of duties is not possible, compensating controls become especially important. These compensating steps help reduce risk in a practical way. Common examples include:
Periodic independent reviews of changes and deployments
Reconciliations and exception reporting reviewed by independent parties
Enhanced logging and periodic signoffs that demonstrate accountability
These measures aren’t perfect substitutes, but they are often realistic for lean teams. More importantly, they show that the organization understands the risk and has taken steps to address it.
What leaders tend to underestimate about documentation
Many audit issues aren’t caused by a complete failure to perform the controls. More often, the work was done but not documented in a way that satisfies the audit requirement.
Some of the most common audit findings are tied to lack of documentation rather than control design itself. Teams often run into trouble by not validating the completeness and accuracy of the reports used for controls, or by not retaining all supporting documentation.
In recent years, validating completeness and accuracy of reports has received much more attention during audits. This has increased the amount of time needed to create adequate control documentation. For already stretched teams, that can create a surprising amount of operational strain.
This is one of the places leaders often underestimate the effort involved. Some requirements may feel overly procedural, but they still matter in an audit context.
Organizations need to be able to show that the reports supporting their controls are reliable and that the control itself was performed when it should have been. It sounds straightforward, but in practice, this is where many teams get tripped up.
What mature organizations do differently
Mature organizations do not stop thinking about controls where audit scope ends, and approach audit readiness as an ongoing discipline rather than a last-minute documentation exercise. Security practices are applied consistently across the environment, even for systems that are not specifically included in the scope of IT audits.
That mindset also applies beyond systems that are formally in scope. Even when an application is not part of a financial statement audit, it still makes sense to apply consistent security practices across the environment. Mature organizations do not stop thinking about controls where audit scope ends.
The strongest organizations understand that some audit requirements are unavoidable, even when they feel disconnected from day-to-day operations. They also recognize that good control procedures should support the business, not stall it. Their goal isn’t to create the most controls, but to build consistent, right-sized controls that reduce risk while keeping the business moving.
That balance isn’t always easy, but it is one of the clearest differences between reactive organizations and mature ones.
What should teams be doing about AI and controls today?
AI is beginning to change the audit and control landscape, even though there is no settled standard yet.
Many teams are exploring how AI can help review logs or speed up parts of the process, but human oversight still matters. If AI tools or agents become part of the processes being audited, organizations will need to understand how those tools affect controls, what risks they introduce, and how to confirm they are working as intended.
There’s also a governance issue that leaders shouldn’t overlook. A company may approve certain AI tools for employee use, but that does not guarantee only approved tools are being used. If confidential company data is entered into non-approved applications, that creates a different category of risk.
Until clearer standards emerge, organizations should treat AI as a tool that may improve efficiency in certain areas, but not as a replacement for human judgment, oversight, and governance.
Final thoughts
A good IT audit is less about checking every box and more about understanding what truly matters: the right scope, controls that address real risks, documentation that stands up to scrutiny, and a thoughtful approach to AI and governance.
Organizations that approach audit this way are better positioned not only to satisfy requirements, but also to strengthen the environment around the systems and processes that matter most.
FAQs
What makes an IT audit effective? An effective IT audit focuses on the systems, controls, and risks that actually matter to the process under review. It goes beyond checklist compliance and helps organizations understand where weaknesses exist and how to address them practically.
Why is audit scope so important? Scope determines where the audit team focuses its attention. If the scope is too narrow, meaningful risks may be missed. If it’s too broad, teams can waste time documenting systems that don’t materially affect the process.
Why do so many audit issues involve documentation? In many cases, the work was performed, but the supporting evidence was incomplete, untimely, or not retained in the right way. That makes documentation one of the most common pain points during an audit.
What can smaller teams do when segregation of duties isn’t realistic? Smaller teams often rely on compensating controls, such as independent reviews, exception reporting, enhanced logging. These controls help reduce risk when strict role separation is not possible.
How should organizations think about AI in an audit environment? Organizations should evaluate where AI is being used, what risks it introduces, and how human oversight will be maintained. AI may improve efficiency, but it shouldn’t replace governance or accountability.
IT Audits don’t have to feel heavy: A more collaborative approach
Audits feel less disruptive when controls and documentation are built into daily work activities, not as separate add-on tasks.
The most effective auditors do more than identify issues; they help teams understand requirements and communicate clearly.
Better coordination across management, internal audit, and external audit can reduce duplicate requests and unnecessary disruption.
A coaching-oriented process helps teams respond with more confidence and makes the experience more constructive.
Audits can often feel heavy because they are perceived as extra work for people whose day jobs don’t always involve documenting controls. When that happens, teams push back and find the whole process frustrating.
An effective IT or controls audit looks different, however. It is collaborative, practical, and designed to help teams move forward with more confidence.
How can audits stop feeling like extra work?
Audits are often seen as extra work by control owners because documenting controls is not usually part of their job function. That perception is real, and it creates a barrier to getting good documentation and reliable answers.
When control documentation is treated as part of regular activities, not as add-ons, audits stop feeling like extra work.
Audits also feel less disruptive when requirements are explained in plain language and built into existing workflows early. That makes controls and documentation easier to manage and helps teams see them as part of the work rather than another inbox item.
What separates a helpful auditor from one who only checks boxes
The difference often comes down to approach. Some audit teams ask a standard set of questions and quickly move to a deficiency if the answer does not fit expectations. A more helpful approach takes time to understand why things are done a certain way and whether the issue is truly a control failure or simply a lack of context.
Coordination reduces repeated work
Strong collaboration between management, internal audit, and external audit helps prevent teams from feeling like they are being audited multiple times. Instead of repeating the same requests months apart, the process becomes more coordinated and far less disruptive.
In practice, that means aligning documentation requests, combining meetings where possible, and maintaining regular touchpoints so teams aren’t answering the same questions repeatedly or fielding new requests every week. Better coordination helps reduce duplicate asks and unnecessary interruptions for both management and technical teams.
How does coaching change the audit experience?
Coaching helps control owners understand what is being asked and respond with confidence.
We work with our clients to guide, coach, and help them through the process the first time, and support the documentation needed to make the audit go smoothly.
By working closely with subject matter experts and understanding systems in depth, we can help turn technical evidence into documentation that both auditors and executives can rely on.
In one recent example, we helped prepare an IT contact for an audit meeting by walking through the types of questions likely to come up and joining the call for support. Afterward, he thanked us for being there, noting how difficult it can be when questions are being fired off quickly. Even when someone knows the answers, audit pressure can make it easy to go off track.
That kind of support makes the process feel more manageable. The value is not just in understanding the controls, but in helping people communicate them clearly and confidently when it matters most.
Final thoughts
Audits don’t have to feel heavy. When the process is collaborative, practical, and coaching-driven, teams spend less time reworking and more time moving forward with confidence.
A stronger audit experience is not just about completing requirements. It is about helping people understand what is needed, reducing repeated work, and making the process more constructive for everyone involved.
Frequently Asked Questions (FAQs)
Will a collaborative audit add more work for my team?
A collaborative audit actually reduces extra work by helping integrate controls documentation into existing workflows and through coaching control owners on what is needed.
What does Behunin & Associates do differently?
We prep client contacts ahead of time, join calls to support answers, and help translate technical responses into audit-ready documentation so teams are not left feeling exposed.
Can better coordination really stop teams from being asked the same questions repeatedly?
Yes. Coordinating documentation requests, meetings, and touchpoints among management, internal audit, and external audit prevents duplicate asks and reduces interruptions to operational teams.